229 Podcasts
Every show in the network: interviews, security programming, and the daily read on what is moving health IT.
New episode · November 5
2 Minute DrillWhen the Apology Is the Phish | 2 Minute Drill with Drex DeFord
On Monday, October 26th, the University of New Mexico Health Sciences Center spotted a cyber event in Albuquerque. By about 12:30, ambulances were being turned away from UNM Hospital — New Mexico's only Level I trauma center, burn unit, and children's hospital — and for about two hours the most seriously injured people in the state had to go somewhere else. That evening a new ransomware gang calling itself Byod claimed the attack, saying they took out 36,000 systems, Active Directory, the entire Microsoft Entra tenant, and walked away with Social Security numbers, payroll, patient information, and Cerner EHR rosters. UNM says the attack hit some end-user devices but did not penetrate core systems or servers, critical systems were coming back online by the 27th, and it made no concessions. Then Byod posted again — this time to apologize, offer free decryption keys for hospitals only, and say they would pay affected patients up to $2,500 each. Tucked into that apology was a line that said they were still going to keep the data, and the offer asked patients to provide proof over Session, an encrypted messaging app. Drex's read: that looks a lot like a phishing lure. UNM moved fast, warning patients and staff not to respond and to report contact to the FBI at ic3.gov. Health systems plan for downtime and diversion; what they often don't plan for is the week after, when attackers or copycats contact patients with fake refunds and fake billing calls. If you get hit tomorrow, is your patient scam warning already written and ready to post on day one? Thanks to Zscaler Healthcare for sponsoring today's show. Drop Drex a note at drex@229project.com. Remember, Stay a Little Paranoid.
The shows
The 229 Podcast
with Bill Russell, Sarah Richardson, Drex DeFord
Newsday
with Bill Russell, Drex DeFord, Sarah Richardson
Executive Interview
with Bill Russell, Sarah Richardson, or Drex DeFord
2 Minute Drill
with Drex DeFord
Solution Showcase
with Bill Russell, Sarah Richardson, or Drex DeFord
UnHack the Podcast
with Drex DeFord
Latest episodes
2 Minute Drill · Nov 5 · 6 min listen
When the Apology Is the Phish | 2 Minute Drill with Drex DeFord
The 229 Podcast · Nov 5 · 23 min listen
Shared Strengths: Roxi Foreman on Governance and Revenue Cycle
Solution Showcase · Nov 4 · 22 min listen
Two Agents Stuck in a Loop | Solution Showcase with Donald Pollard
Newsday · Nov 2 · 43 min listen
Healthcare Isn't Ready for an AI Workforce Yet | Newsday with 229Project
2 Minute Drill · Oct 29 · 6 min listen
When the Internet's Plumbing Bursts | 2 Minute Drill with Drex DeFord
Newsday · Oct 26 · 37 min listen
Using AI Governance as a Shield | Newsday with 229Project
The 229 Podcast · Oct 22 · 22 min listen
Welcome Lori Boisjoli, 229Project's Newest Principal
2 Minute Drill · Oct 21 · 5 min listen
The Ransomware Rescuer Who Paid the Hackers | 2 Minute Drill with Drex DeFord
Newsday · Oct 19 · 34 min listen
Who Gave the Bot Your Password | Newsday with 229Project
2 Minute Drill · Oct 16 · 6 min listen
Evil Tokens and the AI Money Mover Hunt | 2 Minute Drill with Drex DeFord
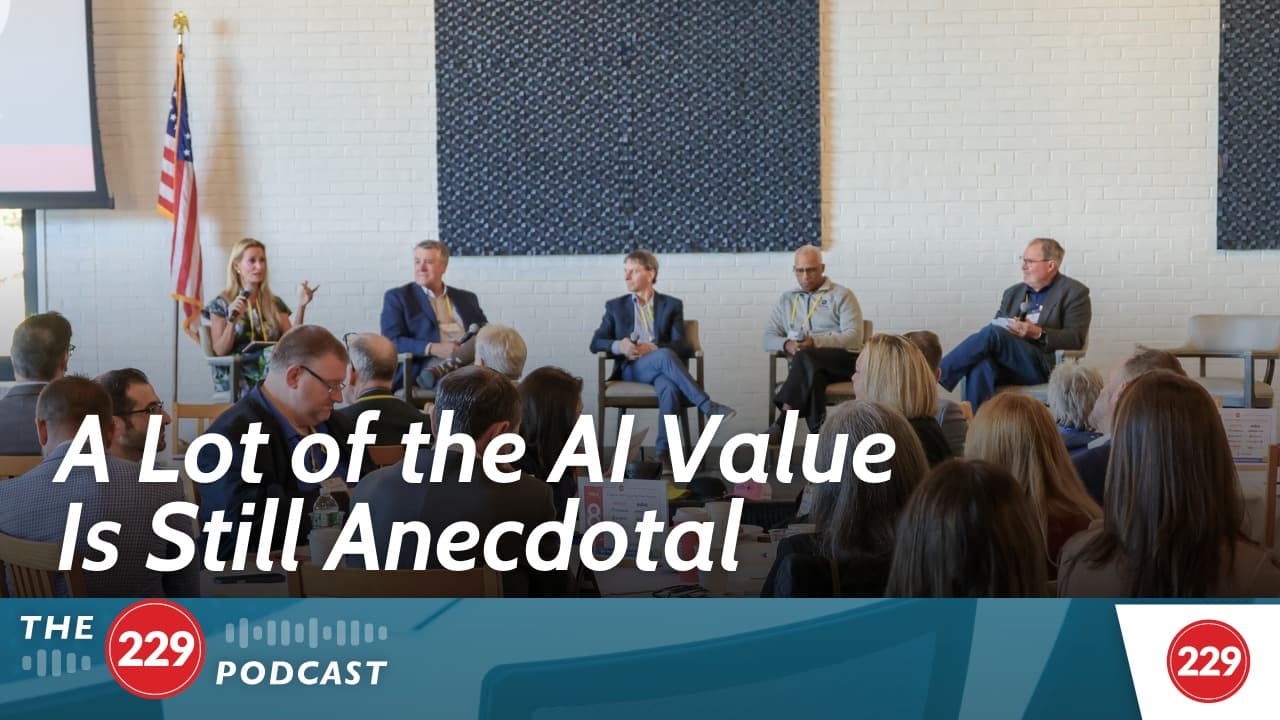
The 229 Podcast · Oct 15 · 29 min listen
A Lot of the AI Value Is Still Anecdotal | The 229 Podcast
Executive Interview · Oct 14 · 19 min listen
Last 3 Years Outgrew the Previous 20 | Executive Interview with Jim Jacobs
2 Minute Drill · Oct 12 · 5 min listen
Who Put Umbreon on the FBI Jobs Site | 2 Minute Drill with Drex DeFord
Newsday · Oct 12 · 36 min listen
I Don't Always Patch. When I Do, It's in Production. | Newsday with 229Project
The 229 Podcast · Oct 8 · 40 min listen
The Clerical Work Should Leave the Visit | The 229 Podcast with Michal Nedoszytko
Newsday · Oct 5 · 29 min listen
10-15% of the Beds Cannot Be Scheduled. | Newsday with Venkat Kavarthapu and 229Project
The 229 Podcast · Oct 1 · 22 min listen
The First Acute System on Epic Orchard | The 229 Podcast with John McDaniel